


 」
 PDF版 Demo


PECB ISO-IEC-27001-Lead-Auditor 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
参照:https://pecb.com/pdf/candidate-handbooks/pecb-candidate-handbook-iso-27001-lead-auditor-mc.pdf
最近、より多くの人たちがISO-IEC-27001-Lead-Auditor資格を取得したい。認定試験によって、自分の能力を高め、職場で良いポジションを求められます。TopexamのISO-IEC-27001-Lead-Auditor試験勉強資料はあなたが成功へのショートカットを与えます。
ISO-IEC-27001-Lead-Auditor資格認定を取得するには苦戦しているあなたによいニュースを持ち込みました。わが社のISO-IEC-27001-Lead-Auditor勉強資料を使っていただければ、認定を取るのはもうそんなに難ししことではありません。認定取得により理想な仕事、希望なポジション、満足な給料がもらえます。自分の未来は自分で舵を取ります。

三つのバージョン
わが社のISO-IEC-27001-Lead-Auditor勉強資料は三つのバージョンがあります。PDF版は印刷できます、印刷してから用紙にメモを取ることができて、とても便利です。ソフト版はいくつかのパソコンにインストールすることができます。本当の試験環境をシミュレーションします。前提としてWindowsシステムにしか使いません。オンライン版は設備に問われず、携帯とかパソコンとカなどの電子設備で使えます。オフライン使用をサポートします。
一年間の無料アップデート
受験問題には変化がありますので、わが社の試験勉強資料もその変化に伴って常にISO-IEC-27001-Lead-Auditor勉強資料を更新し、購入日から一年間に更新された勉強資料をお客様に無料提供します。受験で頭を困らせた人はそんな状態から抜け出したいなら、わが社のISO-IEC-27001-Lead-Auditor試験勉強資料こそあなたの助けになります。
PECB ISO-IEC-27001-Lead-Auditor試験問題集をすぐにダウンロード:成功に支払ってから、我々のシステムは自動的にメールであなたの購入した商品をあなたのメールアドレスにお送りいたします。(12時間以内で届かないなら、我々を連絡してください。Note:ゴミ箱の検査を忘れないでください。)
高い試験通過率
お支払い後、お買い上げのISO-IEC-27001-Lead-Auditor勉強資料をすぐにダウンロードできて、トレーニング資料の勉強と練習をできます。20~30時間で勉強資料を練習すれば、98%~100%の合格率を保証します。ISO-IEC-27001-Lead-Auditor試験に落ちる方は試験通知書で全額を返却できます、或いは他のISO-IEC-27001-Lead-Auditor勉強資料に変えって再勉強します。社会人になってから、受験勉強のために多く時間を割くことがなかなかできない受験者たちには最適です。心配するお客様には、わが社はISO-IEC-27001-Lead-Auditor試験勉強資料デモを用意してます。お買い上げる前に試してください。
PECB Certified ISO/IEC 27001 Lead Auditor 認定 ISO-IEC-27001-Lead-Auditor 試験問題:
問題 #1
Costs related to nonconformities and failures to comply with legal and contractual requirements are assessed when defining:
A. Materiality
B. Reasonable assurance
C. Audit risks
問題 #2
You are conducting a third-party surveillance audit when another member of the audit team approaches you seeking clarification. They have been asked to assess the organisation's application of control 5.7 - Threat Intelligence. They are aware that this is one of the new controls introduced in the 2022 edition of ISO/IEC
27001, and they want to make sure they audit the control correctly.
They have prepared a checklist to assist them with their audit and want you to confirm that their planned activities are aligned with the control's requirements.
Which three of the following options represent valid audit trails?
A. I will check that threat intelligence is actively used to protect the confidentiality, integrity and availability of the organisation's information assets
B. I will review the organisation's threat intelligence process and will ensure that this is fully documented
C. I will ensure that the organisation's risk assessment process begins with effective threat intelligence
D. I will ensure that appropriate measures have been introduced to inform top management as to the effectiveness of current threat intelligence arrangements
E. I will determine whether internal and external sources of information are used in the production of threat intelligence
F. I will review how information relating to information security threats is collected and evaluated to produce threat intelligence
G. I will ensure that the task of producing threat intelligence is assigned to the organisation s internal audit team
H. I will speak to top management to make sure all staff are aware of the importance of reporting threats
問題 #3
Which situation presented below represents a threat?
A. The information security training was provided to only the IT team members of the organization
B. HackX uses and distributes pirated software
C. Hackers compromised the administrator's account by cracking the password
問題 #4
Question:
Which of the following can be considered a minor nonconformity?
A. Lack of multi-factor authentication leaves accounts vulnerable to unauthorized access
B. The information security policy lacks reference to continual ISMS improvement
C. Employees lack training to recognize phishing attempts, increasing malware risks
問題 #5
You are the audit team leader conducting a third-party audit of an online insurance organisation. During Stage
1, you found that the organisation took a very cautious risk approach and included all the information security controls in ISO/IEC 27001:2022 Appendix A in their Statement of Applicability.
During the Stage 2 audit, your audit team found that there was no evidence of the implementation of the three controls (5.3 Segregation of duties, 6.1 Screening, 7.12 Cabling security) shown in the extract from the Statement of Applicability. No risk treatment plan was found.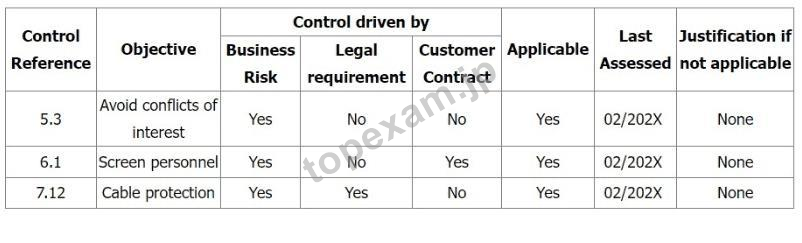
Select three options for the actions you would expect the auditee to take in response to a nonconformity against clause 6.1.3.e of ISO/IEC 27001:2022.
A. Incorporate written procedures for the controls into the organisation's Security Manual.
B. Remove the three controls from the Statement of Applicability.
C. Compile plans for the periodic assessment of the risks associated with the controls.
D. Revisit the risk assessment process relating to the three controls.
E. Implement the appropriate risk treatment for each of the applicable controls.
F. Allocate responsibility for producing evidence to prove to auditors that the controls are implemented.
G. Revise the relevant content in the Statement of Applicability to justify their exclusion.
H. Undertake a survey of customers to find out if the controls are needed by them.
解説:
| 問題 #1 正解: A | 問題 #2 正解: A、B、E | 問題 #3 正解: C | 問題 #4 正解: B | 問題 #5 正解: D、E、G |


 品質保証TopExamは我々の専門家たちの努力によって、過去の試験のデータが分析されて、数年以来の研究を通して開発されて、多年の研究への整理で、的中率が高くて99%の通過率を保証することができます。
 一年間の無料アップデートTopExamは弊社の商品をご購入になったお客様に一年間の無料更新サービスを提供することができ、行き届いたアフターサービスを提供します。弊社は毎日更新の情況を検査していて、もし商品が更新されたら、お客様に最新版をお送りいたします。お客様はその一年でずっと最新版を持っているのを保証します。
 全額返金弊社の商品に自信を持っているから、失敗したら全額で返金することを保証します。弊社の商品でお客様は試験に合格できると信じていますとはいえ、不幸で試験に失敗する場合には、弊社はお客様の支払ったお金を全額で返金するのを承諾します。(
 ご購入の前の試用TopExamは無料なサンプルを提供します。弊社の商品に疑問を持っているなら、無料サンプルを体験することができます。このサンプルの利用を通して、お客様は弊社の商品に自信を持って、安心で試験を準備することができます。

